

Why risks are not an exception, but a norm
In IT projects, risks always arise — regardless of team size, budget, or chosen methodology. New technologies, changing requirements, dependence on external services, the human factor — all of this creates uncertainty that must be managed throughout the entire project lifecycle.
The problem with most unsuccessful projects is not that risks arose, but that they were not managed systematically. Risk management in IT is not a separate activity "at the start," but a continuous process integrated into project management, communication, and decision-making.
What risks are there in IT projects
For effective management, it is important to first correctly classify the risks. In practice, the following groups are most commonly encountered in digital projects.
Technical Risks
Related to architecture, chosen stack, code quality, and integrations. Examples:
- inappropriate architecture for load growth;
- use of unstable or poorly studied technologies;
- complex integrations with external APIs;
- accumulation of technical debt.
Project Risks
Arise from processes and management:
- unrealistic deadlines;
- lack of prioritization;
- frequent changes in requirements without revising the scope;
- weak task formulation.
Business Risks
Related to the goals and expectations of the client:
- unvalidated hypotheses;
- lack of clear product KPI;
- change in business strategy during development.
Communication Risks
One of the most underestimated, yet critical types:
- blurred expectations;
- different interpretations of requirements;
- rare or unsystematic feedback;
- lack of accountability from the client side.
Why risks cannot be «extinguished» at the end of the project
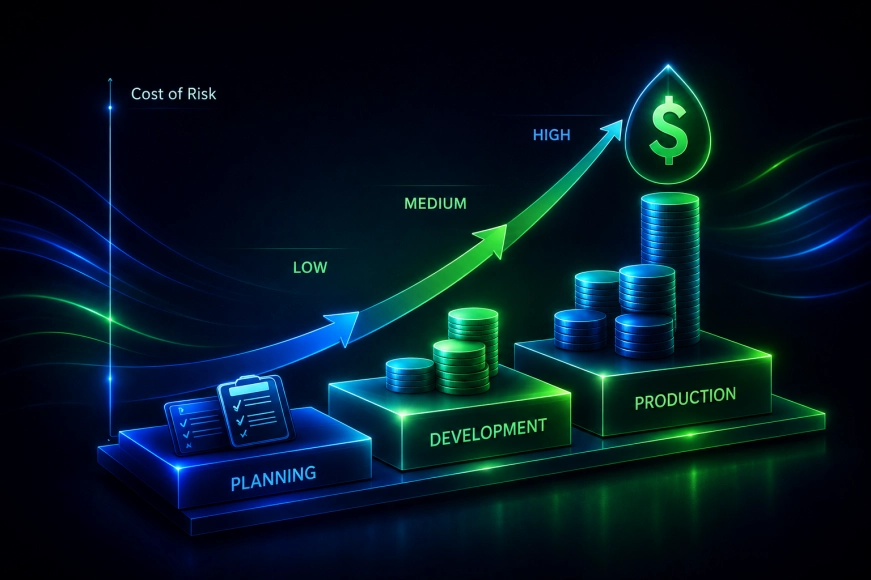
A common mistake is to perceive risks as problems that can be solved «when they arise». In reality, the cost of risk increases exponentially as the project progresses.
At an early stage, risk is a hypothesis.
At the development stage, it is a delay.
At the release stage, it is financial losses and reputational risks.
Therefore, a mature approach implies working with risks in advance, rather than reacting post factum.
Risk Management Process in IT Projects
Risk management is not a document or a table for the sake of formality. It is a cycle of several steps that is repeated throughout the project.
1. Risk Identification
Risks are recorded at the start of the project and supplemented as work progresses. It is important to involve:
- the project manager,
- the technical leader,
- the analyst,
- the client representative.
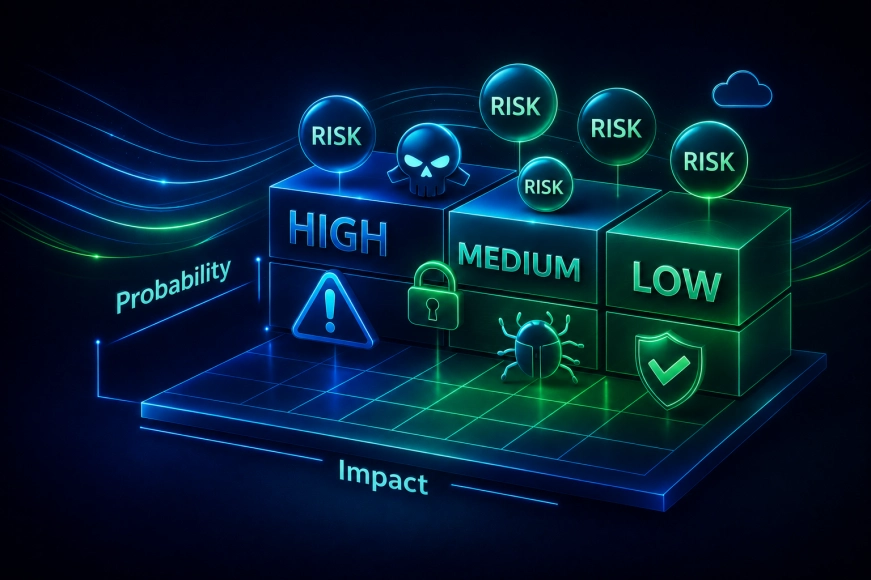
2. Assessment of Probability and Impact
Each risk is assessed based on two parameters:
- probability of occurrence;
- impact on the project (timelines, budget, quality).
This allows focusing on truly critical risks.
3. Response Plan
For each significant risk, a strategy is formed:
- prevention;
- reduction;
- transfer;
- acceptance (conscious).
4. Monitoring
Risks are reviewed regularly — at sprint reviews, status meetings, and planning stages.
Practical example: technical risk and architecture
One of the typical risks — incorrect architecture at the start. It often arises from the desire to "do it faster," without considering scalability and future changes.
In such cases, our team lays down architectural solutions that allow:
- to scale functionality without rewriting the core;
- to isolate changes;
- manage technical debt.
This does not mean complicating the project, but reduces the risk of critical rework in the future.
The role of the team and processes
Risk management is impossible without transparent processes. Methodologies (Scrum, Kanban, hybrid models) do not reduce risks by themselves, but create an environment where risks become visible.
Key practices:
- regular retrospectives;
- short iterations;
- clear prioritization;
- fixing agreements.
Once in the project, it is acceptable to say directly: the RUSO team adheres to an approach where problems are brought up for discussion as early as possible, even if they are uncomfortable.
Communication as a risk management tool
Most critical risks arise not from the code, but from communication. Therefore, it is important to:
- document agreements in writing;
- regularly synchronize on goals;
- discuss changes before their implementation;
- explain the consequences of decisions in business terms.
- Ignoring risks "until it's too late".
- Lack of responsible persons for risks.
- Trying to eliminate all risks at once.
- Underestimating communication risks.
- Lack of regular review.
Conclusions
Risk management in IT projects is not an additional burden, but a way to maintain control over deadlines, budget, and product quality. Projects where risks are identified and discussed in advance develop predictably and sustainably.
Risks cannot be completely eliminated, but they can and should be managed — systematically, transparently, and in collaboration with the client.