

Why data security is the foundation of trust in a SaaS product01
For SaaS platforms, data is a key asset. Users trust the service not only with their files or settings but often:
- commercial information;
- personal data;
- internal processes;
- customer and partner data.
In 2026, data security and storage ceased to be a "technical topic." It is a product and business factor that directly impacts:
- user trust;
- the ability to work with corporate clients;
- legal risks;
- product scaling.
One serious leak or data incident can undermine years of development of a SaaS platform.
In this article, we will discuss:
- which security aspects are critical for SaaS;
- how to approach data storage;
- where dangerous mistakes are most often made.
Security in SaaS: Broader than Protection Against Hacking02
SaaS security is a comprehensive system that includes:
- architecture;
- processes;
- accesses;
- data storage;
- monitoring;
- incident response.
Limiting to just encryption or a firewall — is a dangerous illusion of protection.
A mature SaaS considers security as a continuous process, not a one-time setup.
Access Control and Role Management03
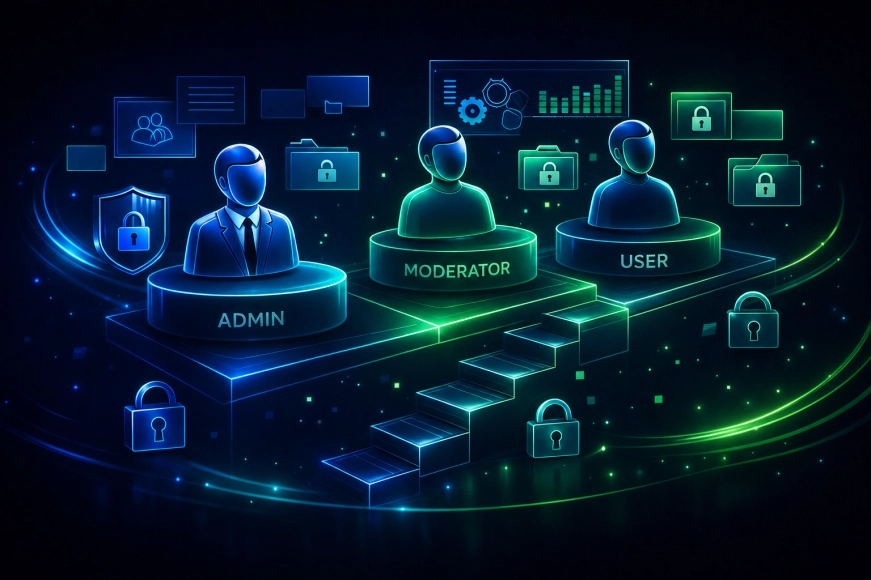
One of the key elements of security is proper access management.
Important:
- clearly define roles;
- minimize default accesses;
- use the principle of least privilege;
- log actions of users and administrators.
Access errors are one of the most common causes of data leaks, especially in B2B SaaS.
Data Storage: Where and How04
The choice of data storage approach affects not only security but also:
- performance;
- scalability;
- total cost of ownership;
- compliance with legal requirements.
Key questions:
- what data is stored;
- where it is physically located;
- how backup is ensured;
- how recovery is performed.
It is important to understand in advance which data is critical and requires a higher level of protection.
Client data isolation05
For SaaS, especially in a multi-tenant model, data isolation is a mandatory requirement.
Main approaches:
- logical isolation at the data level;
- isolation at the schema level;
- dedicated storage for individual clients.
An error in data isolation can lead to the most severe consequences — one client accessing another's data.
Table 1. Approaches to Data Isolation
|
Approach |
Features |
|
Logical Isolation |
Cost-effective, requires strict control |
|
Circuit Isolation |
Balance of security and flexibility |
|
Separate Storage |
Maximum security, higher cost |
Encryption and Data Protection06
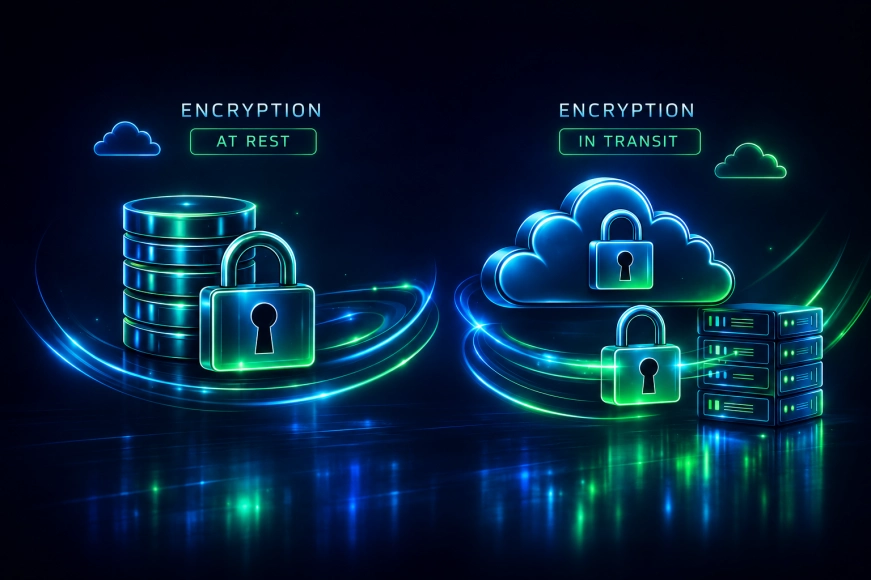
Encryption — a basic but essential level of security.
Important:
- encrypt data at rest;
- protect data in transit;
- manage keys securely;
- regularly review algorithms.
At the same time, encryption does not replace architectural solutions and access control — it is merely one level of protection.
Backup and Recovery07
Storing data is not enough. You need to be prepared to recover it.
Critical points:
- backup regularity;
- storage of copies in different environments;
- recovery testing;
- recovery time control (RTO/RPO).
The absence of a verified recovery plan is often discovered at the most inopportune moment.
Compliance with requirements and regulations08
In 2026, SaaS increasingly operates under:
- personal data requirements;
- industry standards;
- corporate security policies.
It is important to consider:
- data localization;
- storage and deletion rules;
- audit and reporting;
- transparency of processes.
Even if SaaS does not directly handle sensitive data, clients may require compliance with standards.
Incident Monitoring and Response09
Security is not possible without observability.
Mature SaaS:
- monitors access and anomalies;
- records suspicious activities;
- has an incident response plan;
- notifies clients when necessary.
It is important not only to prevent problems but also to be able to respond quickly if they occur.
Typical Security Mistakes in SaaS10
- Security "for later"
- Lack of data isolation
- Excessive access rights
- Irregular backups
- Lack of response plan
These errors are rarely noticed by users until the first serious incident.
How we approach security in SaaS11
Our approach is based on the principle: security is part of the product, not a separate module.
We:
- design architecture with data protection in mind;
- build role-based access models;
- lay down insulation and backup;
- consider the requirements of the business and clients;
- regularly review solutions as the product grows.
The RUSO team considers security as a prerequisite for trust in the SaaS platform.
Conclusions12
Security and data storage in SaaS in 2026 is:
- a strategic decision;
- the foundation of user trust;
- a prerequisite for scaling.
SaaS products that win are those that:
- they think about security from day one;
- they protect data at all levels;
- they are ready for growth and market demands;
- they perceive security as an investment, not an expense.